
更新 2019-05-18
PHPCMS v9 Getshell(apache解析)漏洞EXP
漏洞文件:phpcms\modules\attachment\attachments.php后缀检测:phpcms\modules\attachment\functions\global.func.php Fileext函数是...

不再关注网络安全
漏洞文件:phpcms\modules\attachment\attachments.php后缀检测:phpcms\modules\attachment\functions\global.func.php Fileext函数是...
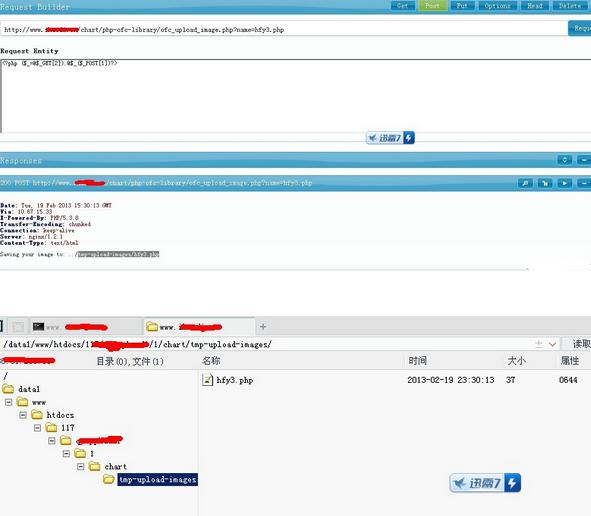
漏洞文件/chart/php-ofc-library/ofc_upload_image.php 利用: /chart/php-ofc-library/ofc_upload_image.php?name=hfy.php hfy.p...
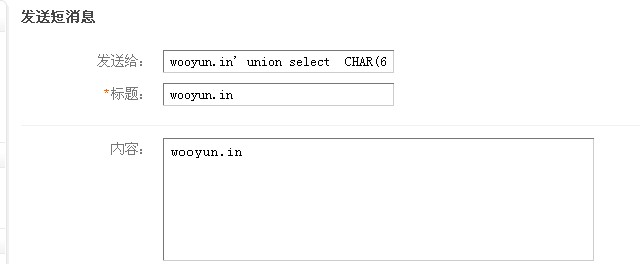
shopex漏洞利用方法: 第一:想办法找到目标网站的绝对路径 http://www.site.com/install/svinfo.php?phpinfo=true http://www.site.co...
+---------------------------------------------------------------------------+ PHPCms V9 GETSHELL 0DAY c0de by testr00ttest hac...
Oblog 4.5-4.6 access&mssql getshell 0day 引导语: 影响范围:4.5 - 4.6 漏洞需求: IIS6.0\开启会员 挖掘作者:henry 绝对...
一,SQl注入漏洞 1,典型的Cookies注入 漏洞文件:Shownews.asp 问题代码: [crayon-6ab077a06b8c3764518015/] 很明显,id参数...
审计代码吧,首先看后台能不能getShell 直接编辑 php文件 写入一句话 所有Sql 语句全部经过一个非常变态的函数 80se...
利用条件:开启注册&&开启投稿 方法 :注册会员 -> 发表文章:内容输入 [crayon-6ab077a06c315790994740/] xss.css内容:...